Finding, testing and protecting the APIs you expose.
Insights · Sep 16, 2026
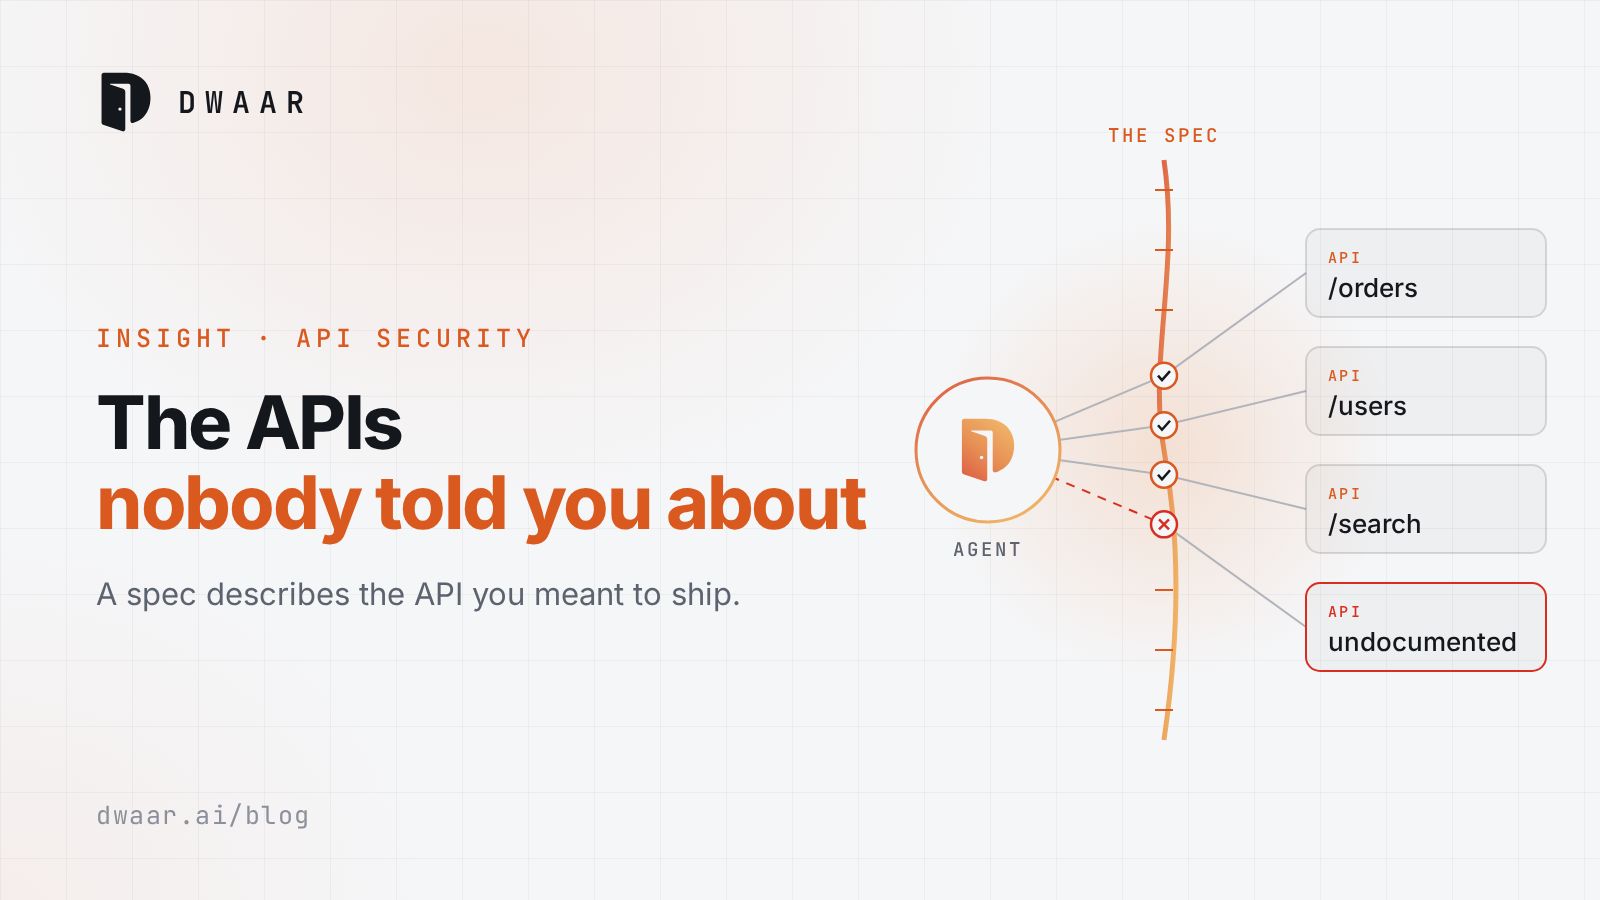
A spec describes the API you meant to ship. Why OWASP's API9 inventory gaps and API1 broken object level authorization stay invisible when you only match known CVEs.