30 posts tagged with "Incidents"
Technical breakdowns of vulnerabilities and attacks, written as they happen.
View All TagsDwaar Blog
October 2026
php2shell: Two Unauthenticated PHP RCEs, One Image Rebuild per Service
CVE-2026-109618 and CVE-2026-109619 give unauthenticated RCE in PHP itself. The fix is 8.2.35, 8.3.36, 8.4.27 or 8.5.12, in every image and on every host that ships PHP.
 Ankush K · 9 min read
CVE-2026-97229: Unauthenticated Code Execution in GitLab Through a Crafted CI/CD Regular Expression
GitLab CVE-2026-97229 could let an unauthenticated user run code on the server via a crafted CI/CD regular expression. GitLab scores it 10.0. Fixed in 19.2.8, 19.3.5 and 19.4.2.
Ankush K · 10 min read
Argo CD Repo Server Command Execution Through Kustomize
Two Critical Argo CD advisories show Kustomize builds running commands in the repo-server, reachable with only Application get. Fixed in 3.3.15, 3.4.10, 3.5.4 and 3.6.0-rc2.
Ankush K · 7 min read
CVE-2026-94603: A Podman Image Annotation Switches Off the Sandbox You Asked For
On rootful Podman from 4.4.0, one image annotation makes podman run ignore flags such as --cap-drop=ALL. Podman 5.8.8 and 6.1.3 remove the feature.
Ankush K · 8 min readSeptember 2026
MCP SDK OAuth Clients Could Send Credentials to a Server-Chosen Authorization Server
The official MCP Python and TypeScript OAuth clients let a connected server steer credentials to an authorization server it chose. Upgrading alone does not finish the fix.
Ankush K · 8 min read
CVE-2026-94545: One Satori Escaping Bug, Moderate in the Library and Critical in next/og
One Satori SVG escaping flaw, scored Moderate 5.3 by Satori and Critical 9.5 by Next.js. Fixed in satori 0.33.5 and next 16.3.6. Only some apps can reach the critical path.
Ankush K · 8 min readAugust 2026
ContextForge CVE-2026-53710 and Chainlit CVE-2026-45018: Allowlists and Denylists Around MCP Keep Failing
A sandbox escape in ContextForge's python_sandbox_server and an unauthenticated command injection in Chainlit's /mcp endpoint both beat text checks. Fixed in 1.0.2 and 2.12.0.
Ankush K · 9 min read
vm2 Again: Sandbox Escapes and the Incomplete Fix Problem
vm2 3.11.6 closes two critical sandbox escapes, CVE-2026-47686 and CVE-2026-47698. The second bypasses a fix that shipped in May, so upgrading then did not close it.
Ankush K · 8 min read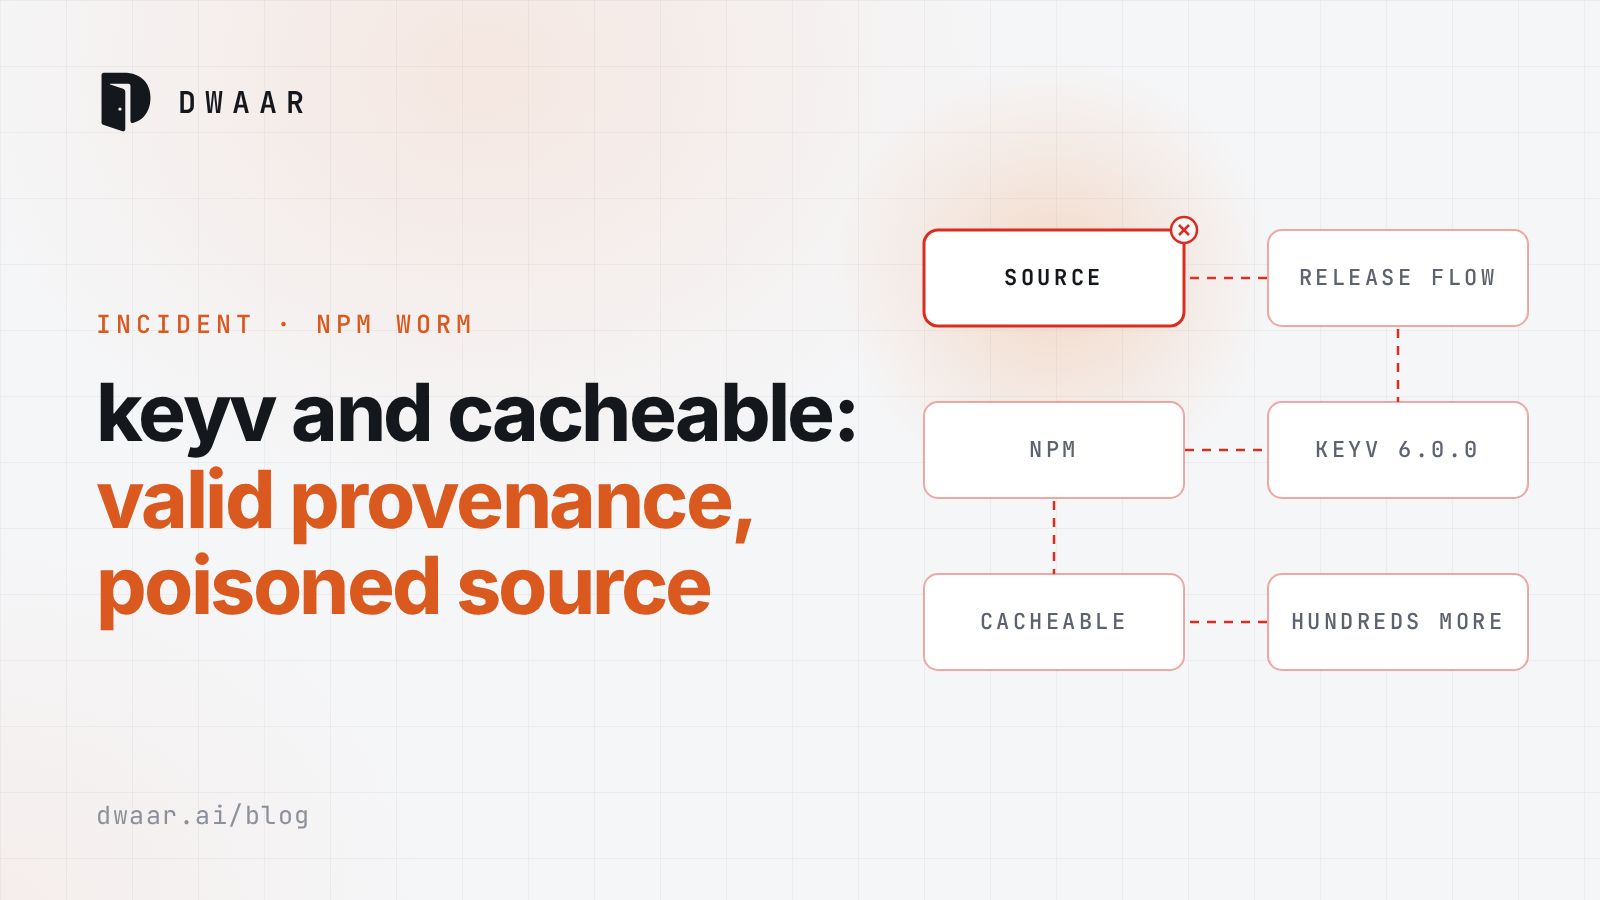
The keyv and cacheable npm Worm: Valid Provenance, Poisoned Source
A malicious keyv 6.0.0 reached npm through the project's real release workflow with valid provenance, then a worm spread through the Cacheable packages and hundreds more.
Ankush K · 9 min read
The 100 BTC Dare Misses the Real Agent-Security Lesson
Why the 100 BTC dare matters less than the security boundary around AI agents and how to control egress, tools, approvals and runtime actions.
 Saurabh · 8 min read
July 2026
CVE-2026-66066: Rails Active Storage File Read Through libvips
A crafted upload may read server files through libvips in Rails Active Storage. Fixed in 7.2.3.2, 8.0.5.1 and 8.1.3.1, which need libvips 8.13 or later. Rotate your secrets too.
Ankush K · 9 min read
wp2shell: An Unauthenticated RCE Chain in WordPress Core
Two WordPress core bugs chain into unauthenticated RCE. Fixes shipped July 17, CISA listed both on July 21, and WPScan and CISA score the two CVEs in opposite order.
Ankush K · 12 min read
The Hugging Face Breach Is a Preview: Why Guardrails Must Live Outside the Model
Hugging Face's July 2026 incident shows what happens when the model supply chain itself is compromised. Scope-based identity isn't enough — agentic security needs zero-trust, intent-based identity and a physically separate guardrail engine.
Ankush K · 12 min read
AsyncAPI: Trojaned npm Packages With Valid Provenance
Five malicious @asyncapi npm versions shipped on 2026-07-14 through the project's own release pipeline, with valid provenance and no install script.
Ankush K · 10 min read
GitLost: When the Agent's Token Scope Decides What a Public Issue Can Steal
Researchers showed a public issue steering a GitHub Agentic Workflow into posting a private repo's README as a public comment. No CVE. GitHub's gh-aw project began shipping a mitigation on July 8.
Ankush K · 11 min readJune 2026
Cordyceps: Exploitable GitHub Actions Workflows in Over 300 Repositories
Researchers report more than 300 exploitable repositories from a class of GitHub Actions flaws, including chains of individually valid workflows. No CVE, no versions to patch, no in-the-wild use reported.
Ankush K · 8 min read
A vLLM Dockerfile Dependency Confusion: How One --extra-index-url Put the Official Image at Risk (GHSA-jrf6-vqxq-pjv2)
vLLM's Dockerfile mixed --extra-index-url with uv's unsafe-best-match, exposing vllm/vllm-openai builds below 0.22.1 to dependency confusion. The advisory reports no exploitation.
Ankush K · 8 min read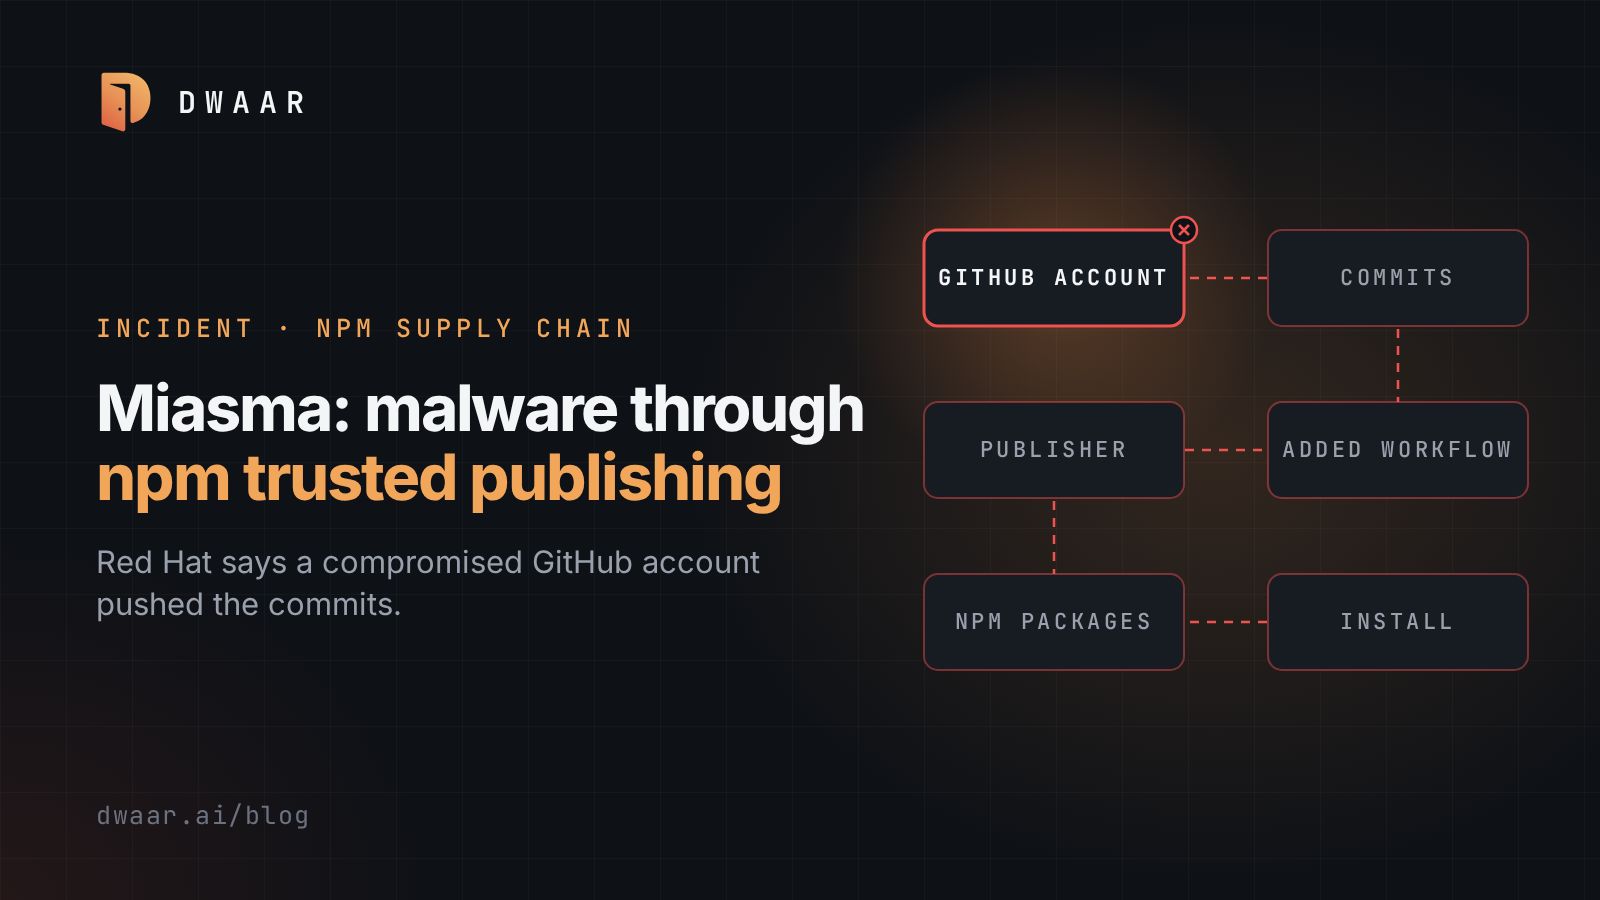
Miasma: How a Compromised Red Hat GitHub Account Published Malware Through npm Trusted Publishing
Red Hat says a compromised GitHub account pushed unauthorized commits. Reports say an added workflow then published malicious @redhat-cloud-services packages through npm trusted publishing.
Ankush K · 8 min readMay 2026
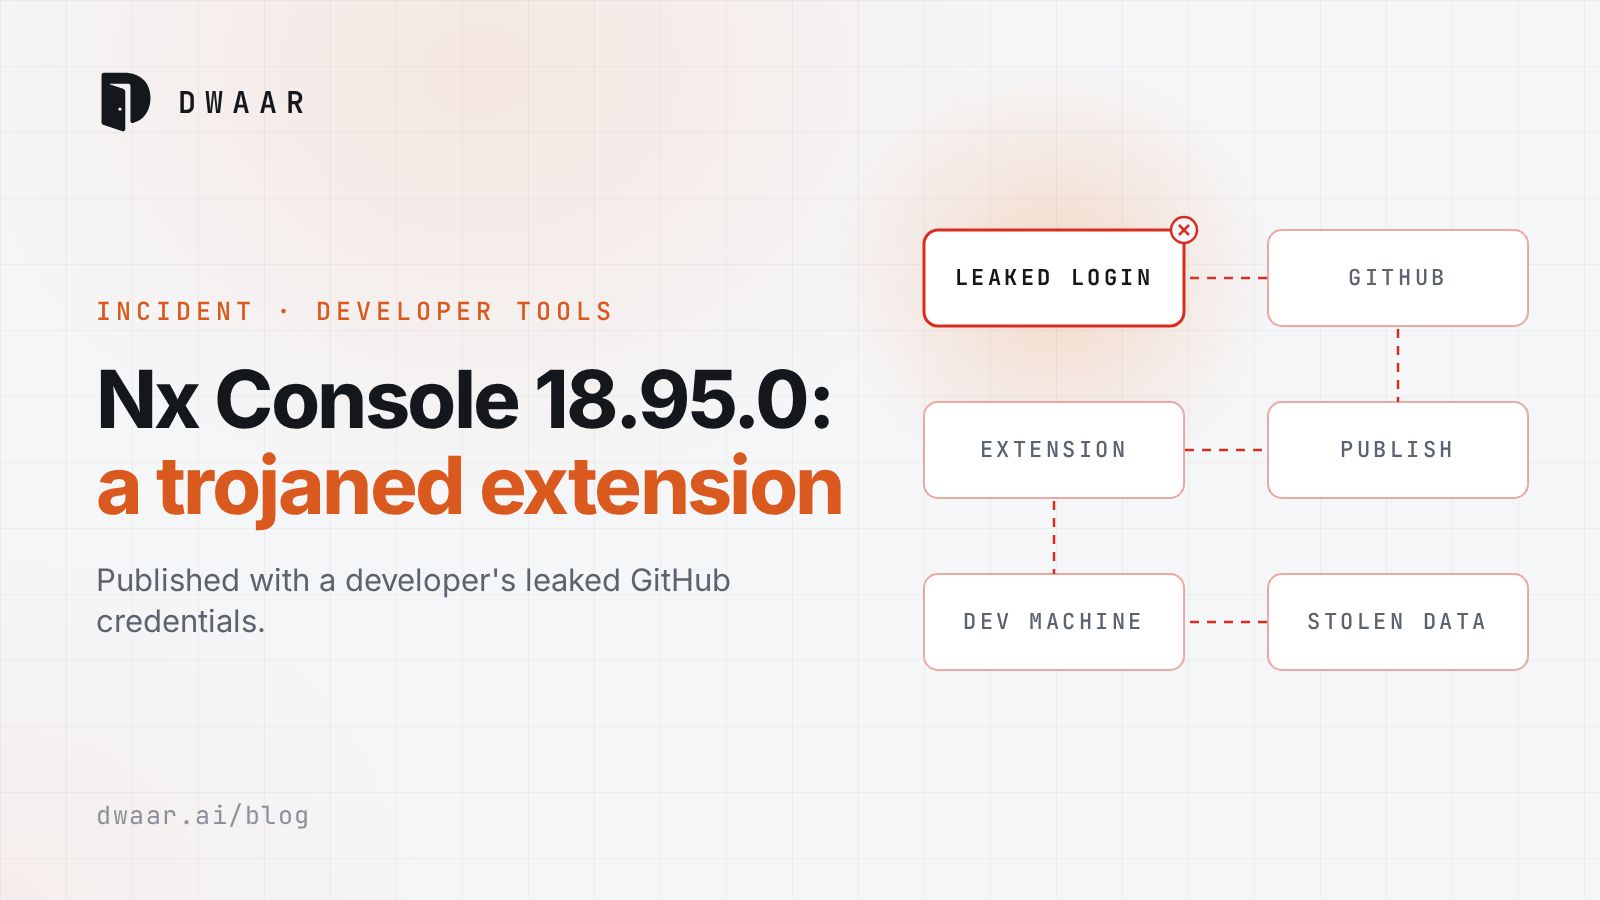
Nx Console 18.95.0: A Trojaned VS Code Extension Published With Stolen Credentials
Nx Console 18.95.0 was trojaned on 18 May 2026 using a developer's leaked GitHub credentials. What it stole, how to check your machines, and what GitHub has and has not said.
Ankush K · 9 min read
NGINX Rift, CVE-2026-42945: An 18-Year-Old Heap Overflow in the Rewrite Module
A heap overflow in the NGINX rewrite module, fixed on 13 May 2026, needs a specific rewrite pattern to trigger. Check versions, images and config.
Ankush K · 9 min read
The TanStack npm Compromise: Actions Cache Poisoning and a Stolen OIDC Token Behind a Legitimate Trusted Publisher
On 2026-05-11, 84 malicious versions of 42 @tanstack npm packages shipped through TanStack's real trusted publisher, using a poisoned Actions cache and an OIDC token read from runner memory.
Ankush K · 9 min read
Bleeding Llama, CVE-2026-7482: An Unauthenticated Heap Leak in Ollama
An out-of-bounds read in Ollama before 0.17.1 lets an unauthenticated client push heap memory to its own registry. Upgrade, then find every server you run and who can reach it.
Ankush K · 10 min readApril 2026
Copy Fail, CVE-2026-31431: A Page-Cache Write From a Container to Root
A logic flaw in the Linux kernel's AF_ALG path lets an unprivileged local user write into the page cache of any readable file and gain root. Patch the host kernel, not the image.
Ankush K · 8 min read
MCP STDIO: When Command Execution Is the Design
MCP's stdio transport launches a configured command. Researchers tie that to flaws in tools such as Flowise, fixed in 3.1.0, and Agent Zero 0.9.8. They say the underlying flaw remains.
Ankush K · 8 min read
CVE-2026-34197: A 13-Year-Old ActiveMQ Bug, Found With AI Assistance
An ActiveMQ Classic management API lets console users run code on the broker. Fixed in 5.19.4 and 6.2.3. The finder says the bug sat for 13 years and was found with Claude.
Ankush K · 8 min read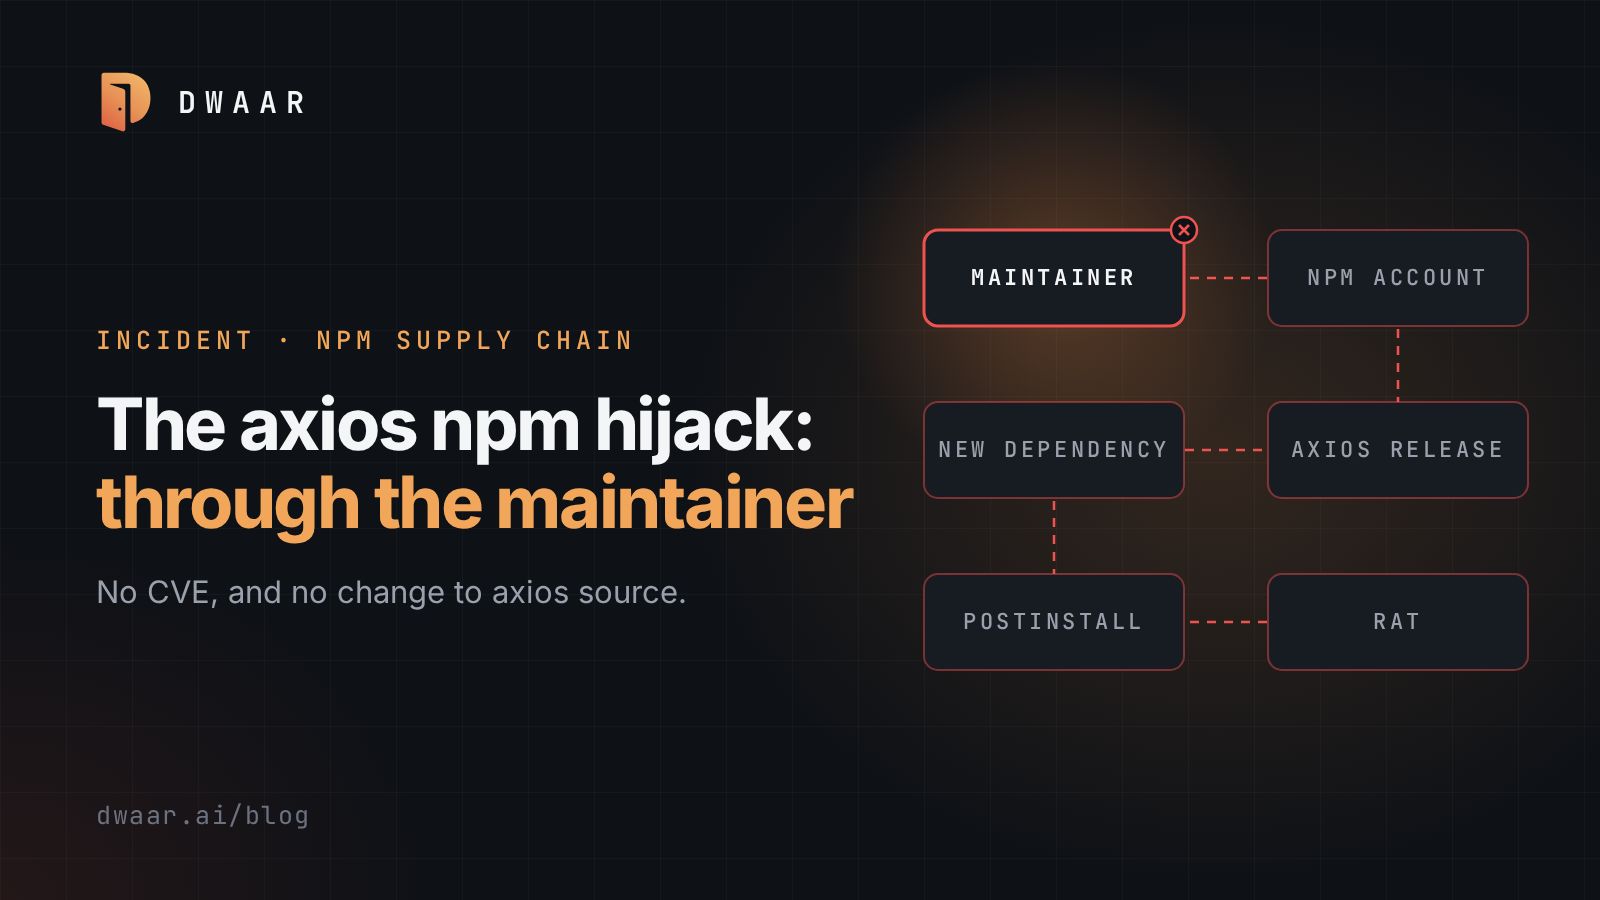
The axios npm Hijack: When the Attack Goes Through the Maintainer
Two axios releases on npm carried a RAT through a postinstall hook in a new dependency, with no CVE and no change to axios source. What to check, and what lockfiles and release age buy you.
Ankush K · 8 min readMarch 2026
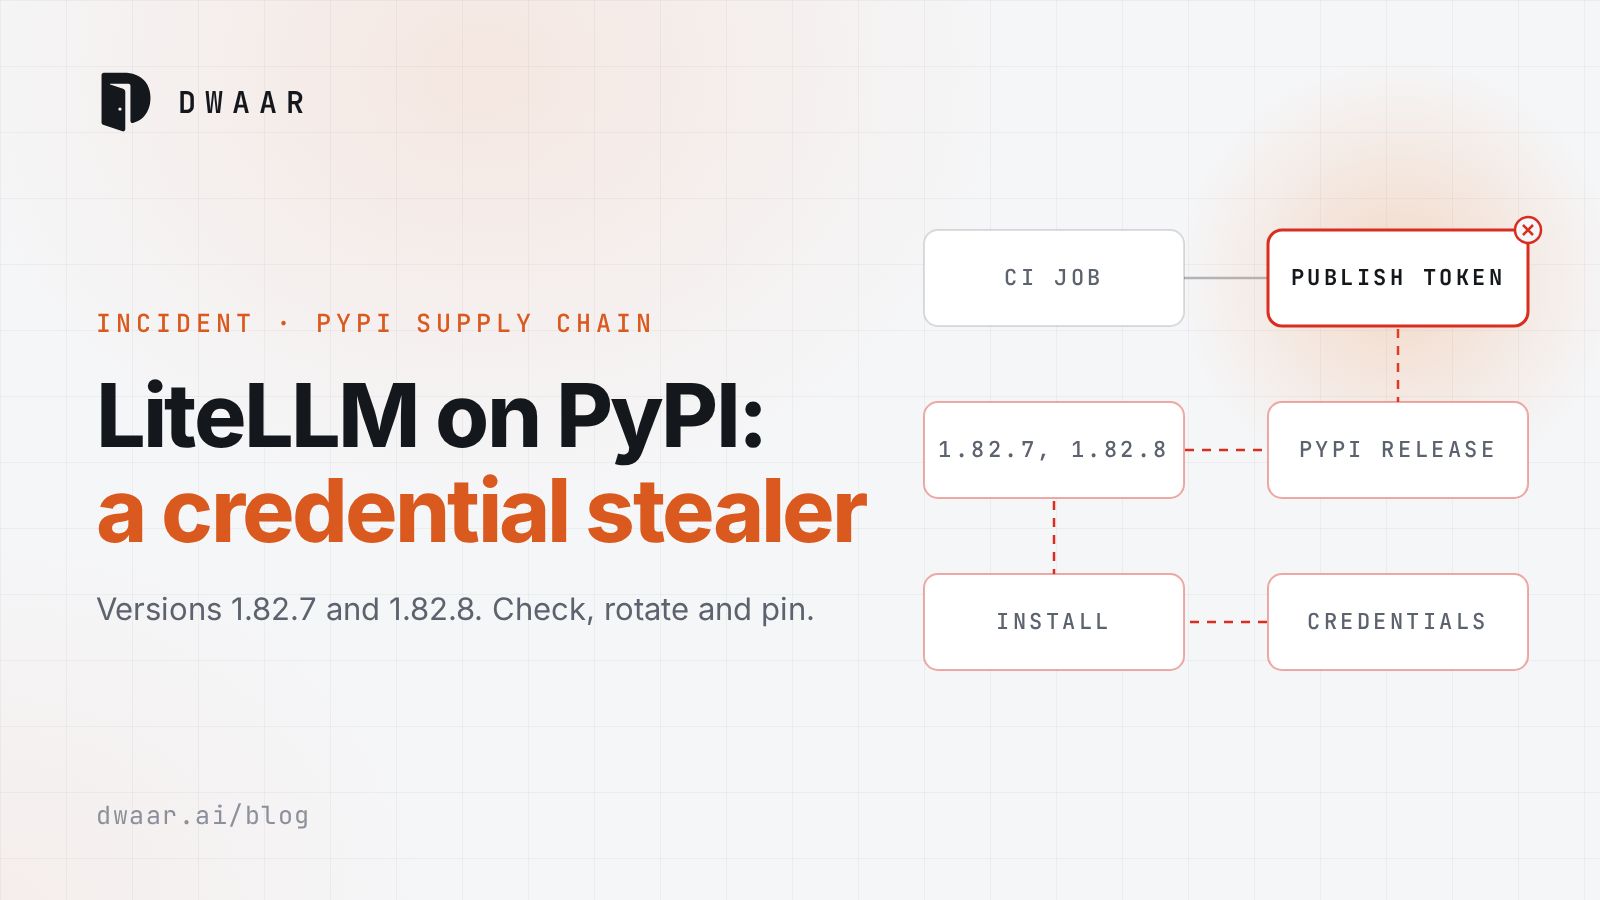
The LiteLLM PyPI Compromise: How Stolen CI Credentials Reportedly Reached an AI Gateway
litellm 1.82.7 and 1.82.8 on PyPI carried a credential stealer, which the maintainers believe traces to a publishing token exposed in CI. What to check, rotate and pin.
Ankush K · 9 min read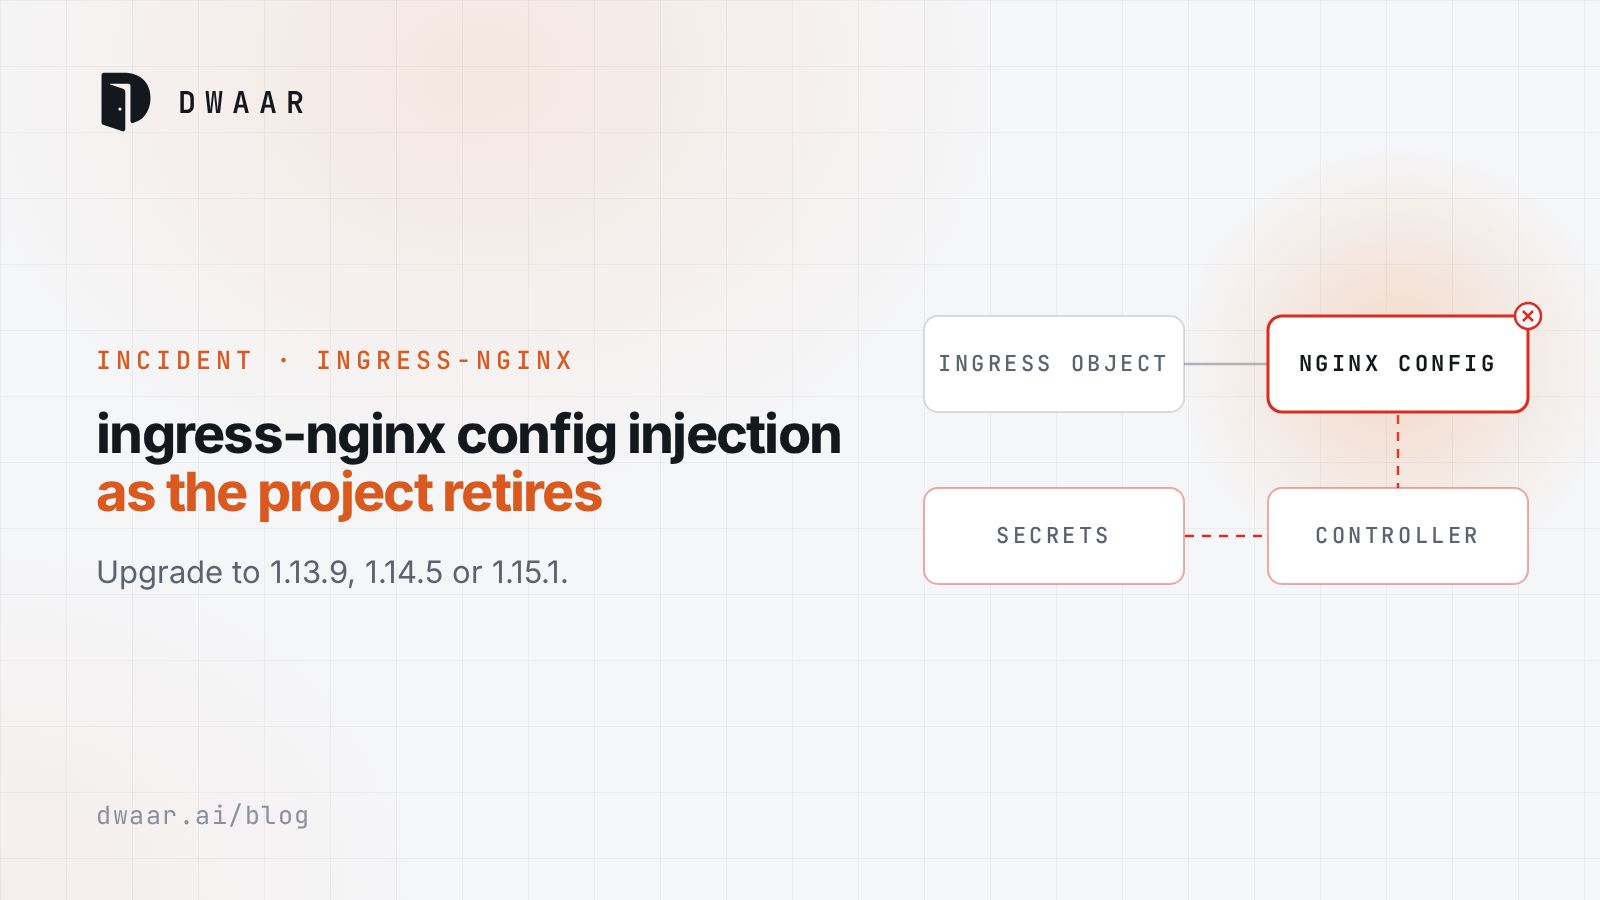
ingress-nginx CVE-2026-3288 and CVE-2026-4342: Config Injection as the Project Retires
Two ingress-nginx advisories describe nginx config injection via Ingress objects, with cluster-wide Secret access by default, as maintenance ends. Upgrade to 1.13.9, 1.14.5 or 1.15.1.
Ankush K · 10 min read
CVE-2026-33017: Langflow's Public Flow Endpoint Runs Unauthenticated Code, and No Stable Release Fixes It
An unauthenticated Langflow RCE has a public advisory and proof of concept, and as of March 19 no stable langflow release on PyPI carries the fix.
Ankush K · 7 min read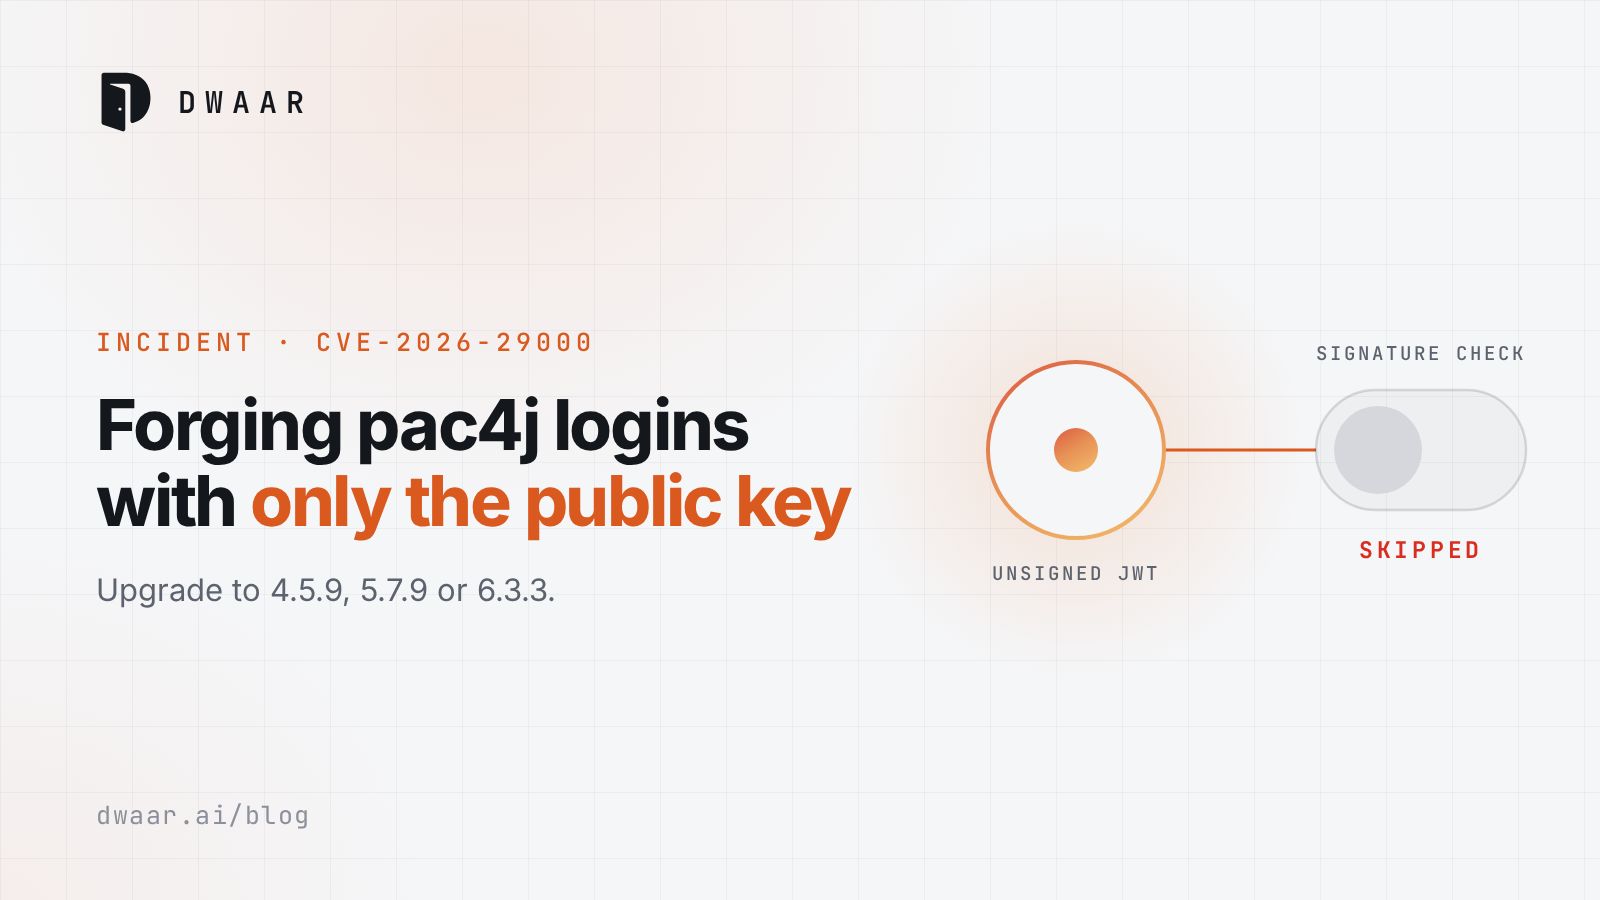
CVE-2026-29000: Forging pac4j-jwt Logins With Only the Public Key
pac4j-jwt skipped signature checks on unsigned tokens inside encrypted JWEs, so an RSA public key could forge a login. Upgrade to 4.5.9, 5.7.9 or 6.3.3.
Ankush K · 9 min read