11 posts tagged with "Open source"
Risk in the dependencies you did not write.
View All TagsDwaar Blog
November 2026
October 2026
September 2026
August 2026
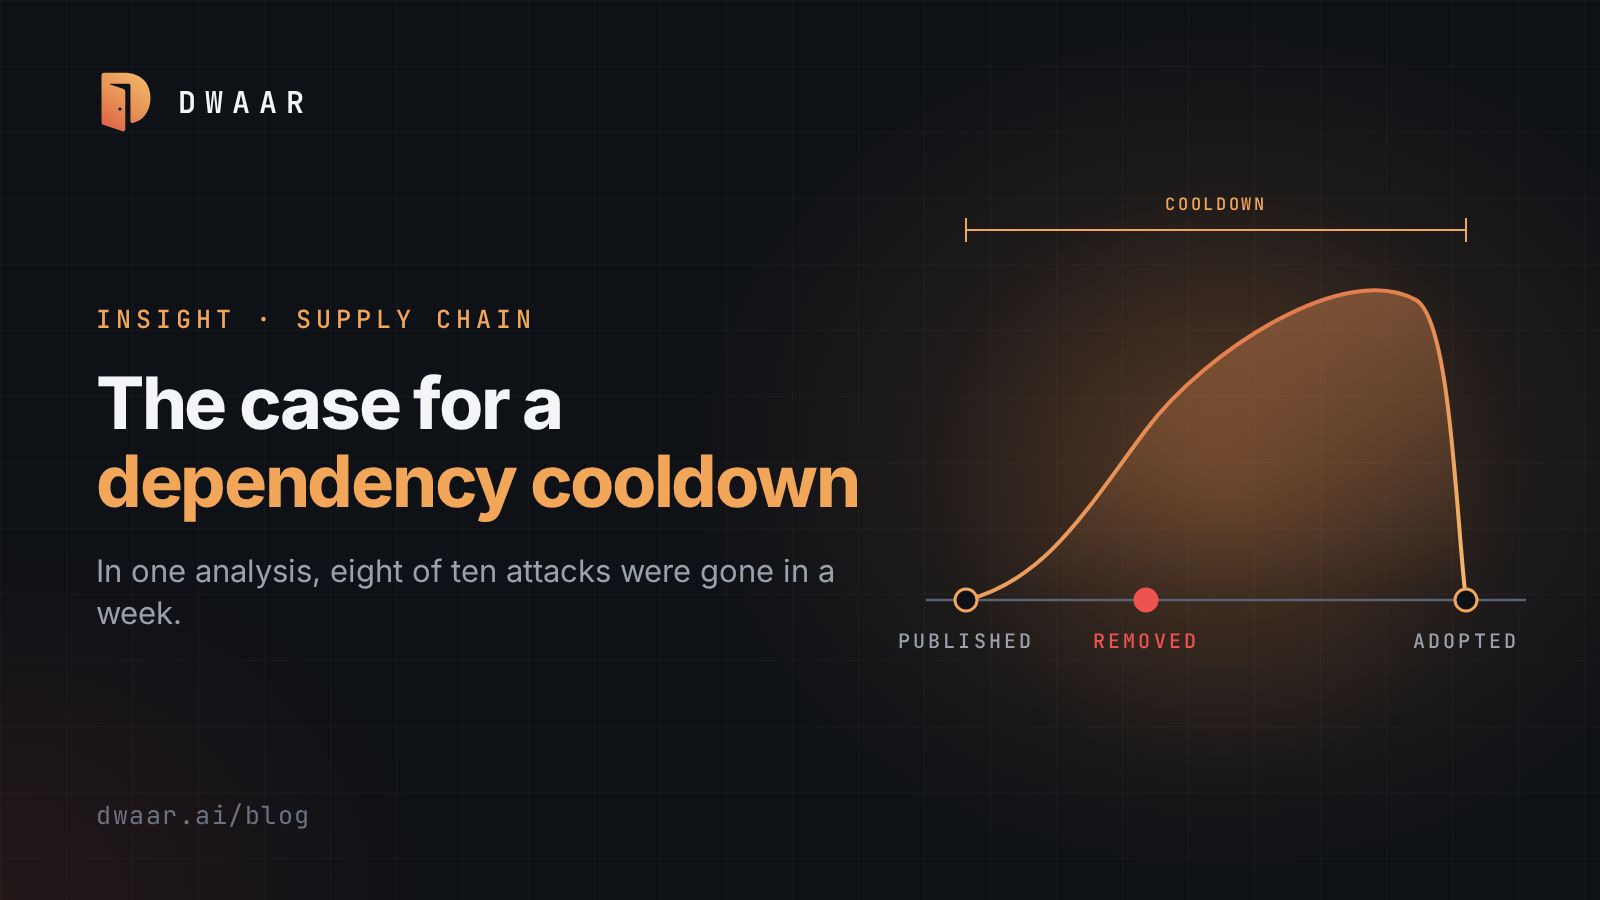
The Case for a Dependency Cooldown
In one analysis of ten supply chain attacks, eight were removed in under a week. Why waiting before adopting a new version works, where it fails, and how to exempt security fixes.
 Ankush K · 9 min read
vm2 Again: Sandbox Escapes and the Incomplete Fix Problem
vm2 3.11.6 closes two critical sandbox escapes, CVE-2026-47686 and CVE-2026-47698. The second bypasses a fix that shipped in May, so upgrading then did not close it.
Ankush K · 8 min read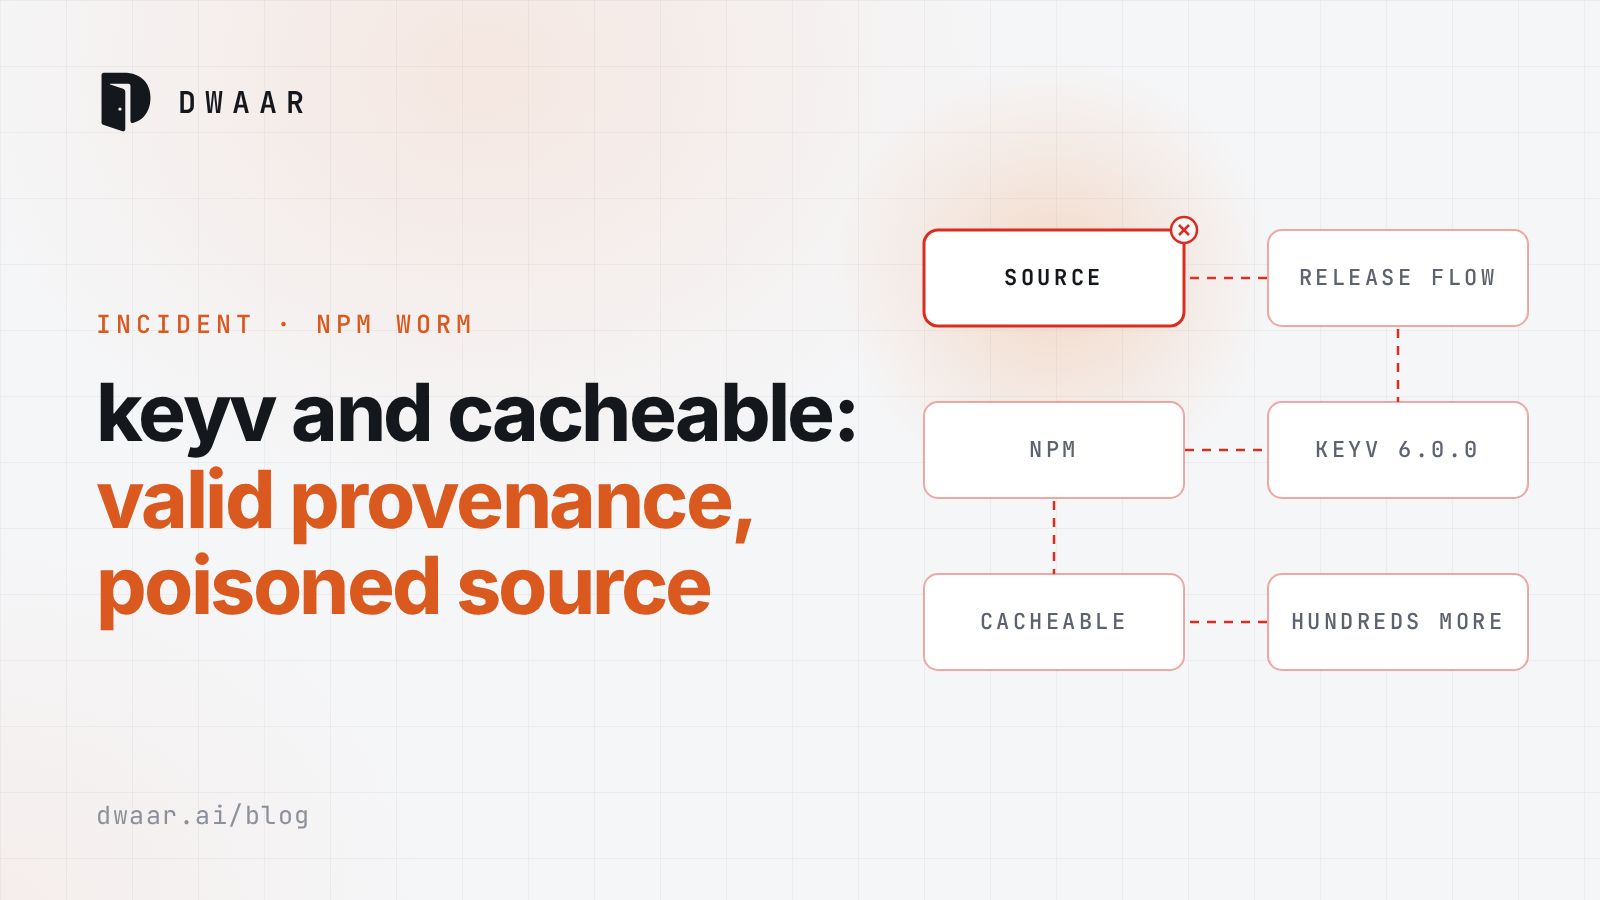
The keyv and cacheable npm Worm: Valid Provenance, Poisoned Source
A malicious keyv 6.0.0 reached npm through the project's real release workflow with valid provenance, then a worm spread through the Cacheable packages and hundreds more.
Ankush K · 9 min readJune 2026
April 2026
A Vulnerable Package and a Malicious Package Are Different Problems
The OSV and GitHub records for the poisoned axios and LiteLLM releases list no CVE. Malicious packages need a different signal, clock and response from vulnerable ones.
Ankush K · 9 min read
CVE-2026-34197: A 13-Year-Old ActiveMQ Bug, Found With AI Assistance
An ActiveMQ Classic management API lets console users run code on the broker. Fixed in 5.19.4 and 6.2.3. The finder says the bug sat for 13 years and was found with Claude.
Ankush K · 8 min read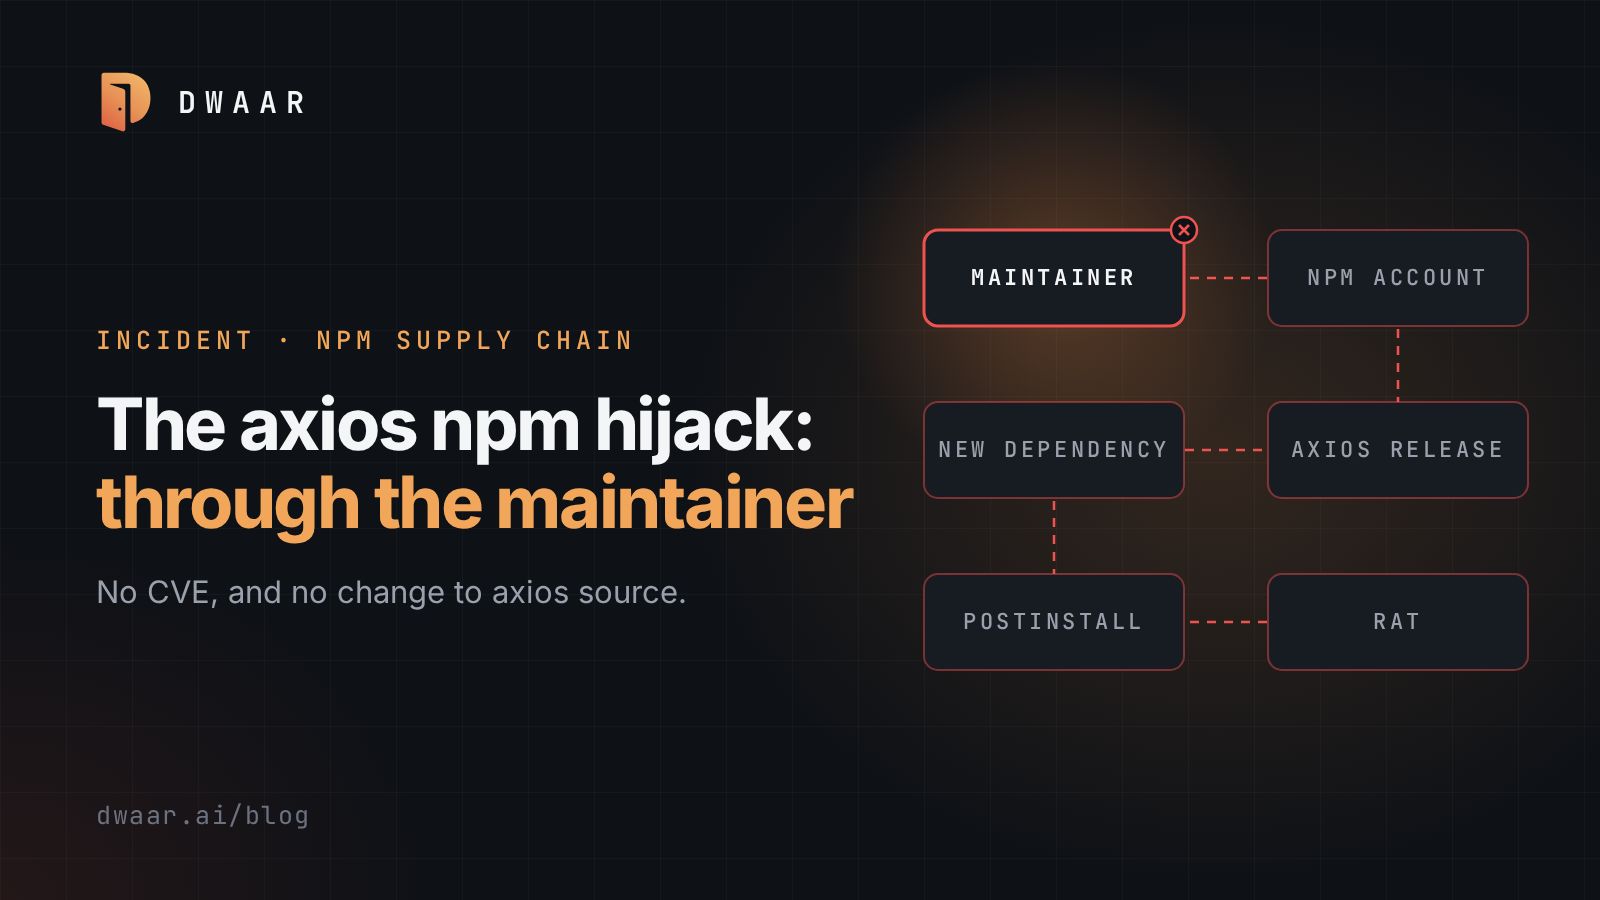
The axios npm Hijack: When the Attack Goes Through the Maintainer
Two axios releases on npm carried a RAT through a postinstall hook in a new dependency, with no CVE and no change to axios source. What to check, and what lockfiles and release age buy you.
Ankush K · 8 min read