9 posts tagged with "CI/CD"
The build pipeline as an attack surface.
View All TagsDwaar Blog
October 2026
CVE-2026-97229: Unauthenticated Code Execution in GitLab Through a Crafted CI/CD Regular Expression
GitLab CVE-2026-97229 could let an unauthenticated user run code on the server via a crafted CI/CD regular expression. GitLab scores it 10.0. Fixed in 19.2.8, 19.3.5 and 19.4.2.
 Ankush K · 10 min read
Argo CD Repo Server Command Execution Through Kustomize
Two Critical Argo CD advisories show Kustomize builds running commands in the repo-server, reachable with only Application get. Fixed in 3.3.15, 3.4.10, 3.5.4 and 3.6.0-rc2.
Ankush K · 7 min readJuly 2026
AsyncAPI: Trojaned npm Packages With Valid Provenance
Five malicious @asyncapi npm versions shipped on 2026-07-14 through the project's own release pipeline, with valid provenance and no install script.
Ankush K · 10 min read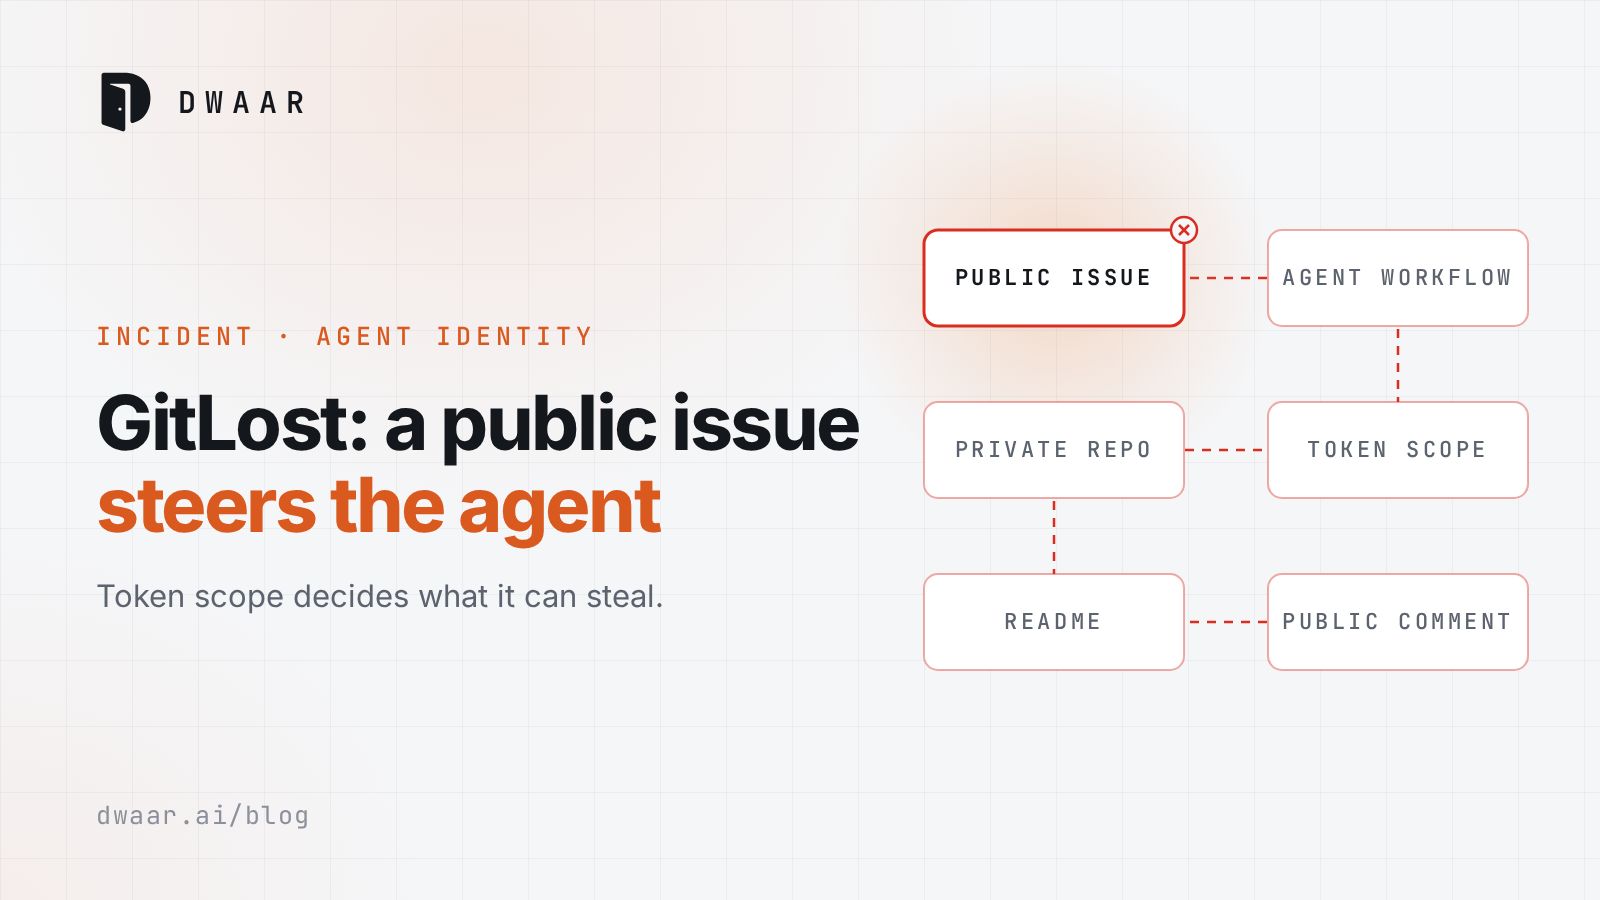
GitLost: When the Agent's Token Scope Decides What a Public Issue Can Steal
Researchers showed a public issue steering a GitHub Agentic Workflow into posting a private repo's README as a public comment. No CVE. GitHub's gh-aw project began shipping a mitigation on July 8.
Ankush K · 11 min readJune 2026
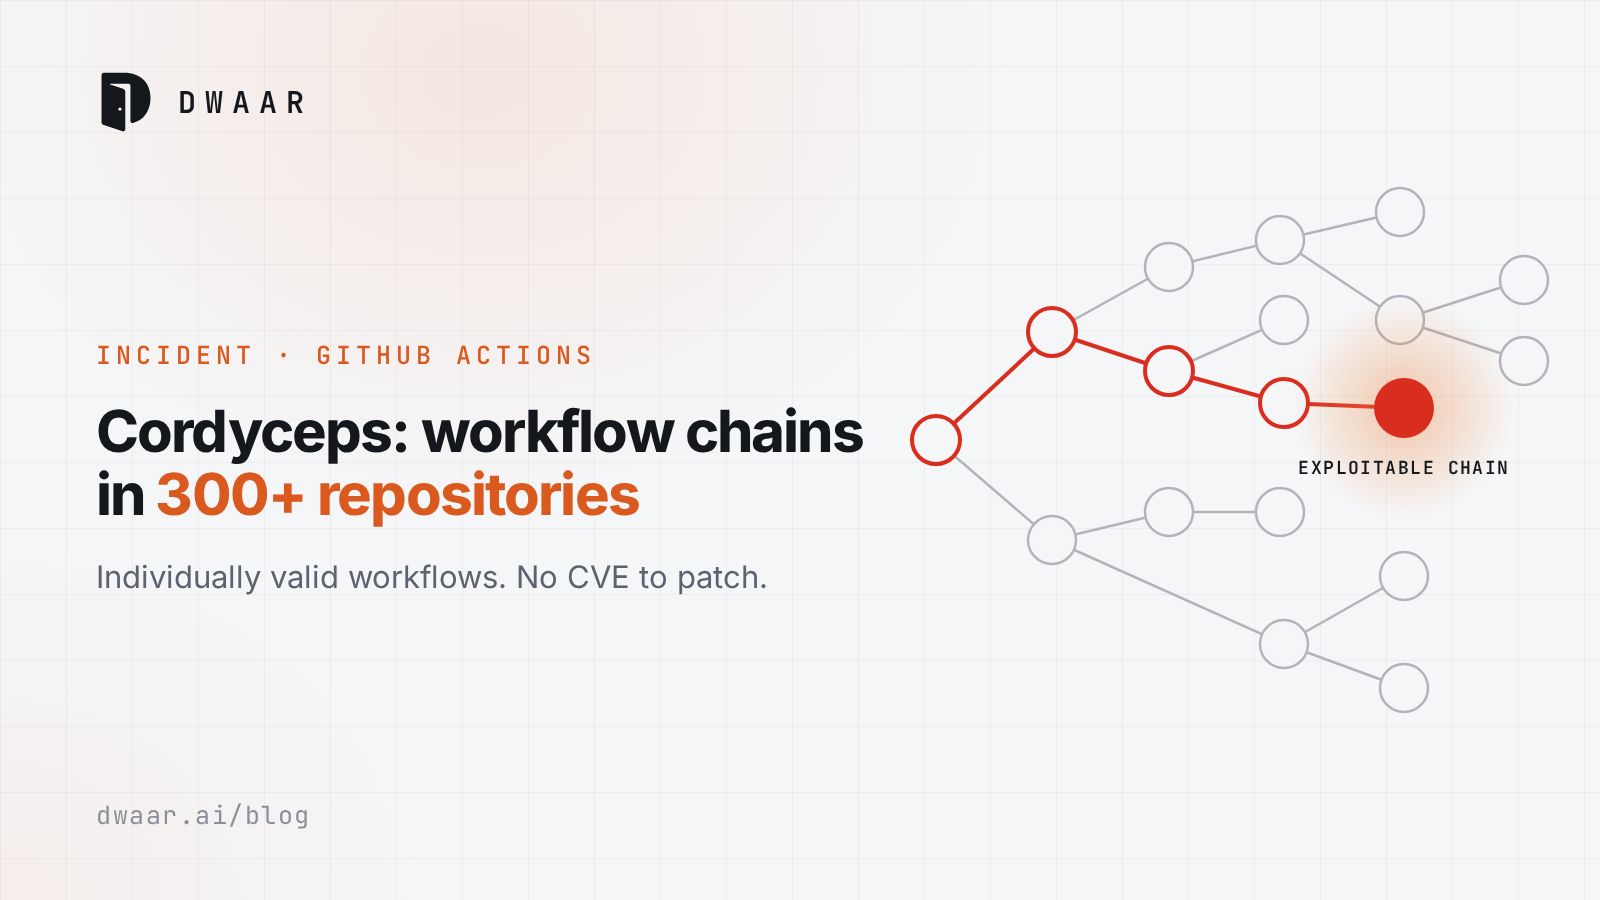
Cordyceps: Exploitable GitHub Actions Workflows in Over 300 Repositories
Researchers report more than 300 exploitable repositories from a class of GitHub Actions flaws, including chains of individually valid workflows. No CVE, no versions to patch, no in-the-wild use reported.
Ankush K · 8 min read
Your CI Pipeline Is Production
CI jobs hold publish tokens, cloud credentials and repository write access. Moved tags, pull_request_target, shared caches and stored secrets have all turned that authority on users.
Ankush K · 9 min readMay 2026
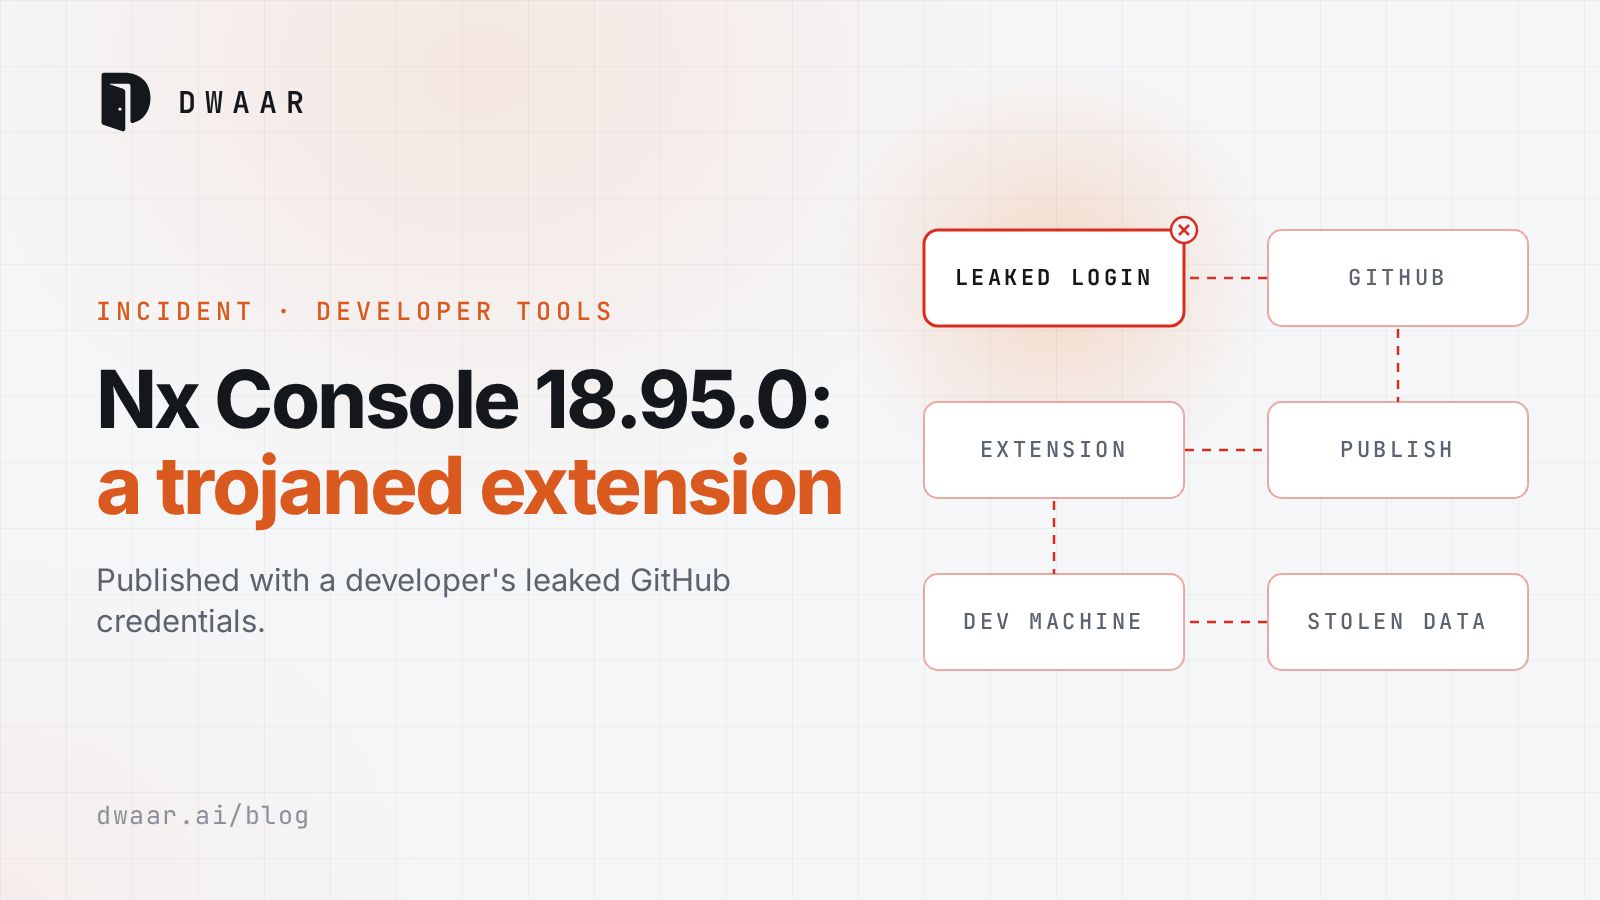
Nx Console 18.95.0: A Trojaned VS Code Extension Published With Stolen Credentials
Nx Console 18.95.0 was trojaned on 18 May 2026 using a developer's leaked GitHub credentials. What it stole, how to check your machines, and what GitHub has and has not said.
Ankush K · 9 min read
The TanStack npm Compromise: Actions Cache Poisoning and a Stolen OIDC Token Behind a Legitimate Trusted Publisher
On 2026-05-11, 84 malicious versions of 42 @tanstack npm packages shipped through TanStack's real trusted publisher, using a poisoned Actions cache and an OIDC token read from runner memory.
Ankush K · 9 min read