8 posts tagged with "Remediation"
Closing the gap between finding a problem and fixing it.
View All TagsDwaar Blog
October 2026
Stop Counting Vulnerabilities
A count of open findings measures backlog, not risk. Measure time to fix what is exploited or exposed, coverage of what you own and repeat findings, and know how each gets gamed.
 Ankush K · 9 min read
php2shell: Two Unauthenticated PHP RCEs, One Image Rebuild per Service
CVE-2026-109618 and CVE-2026-109619 give unauthenticated RCE in PHP itself. The fix is 8.2.35, 8.3.36, 8.4.27 or 8.5.12, in every image and on every host that ships PHP.
Ankush K · 9 min read
A Waiver Should Expire
Risk acceptance with no end date is a hidden backlog. What a waiver should record, what should reopen it, and why suppressing noise is a different decision.
Ankush K · 8 min readAugust 2026
July 2026
April 2026
March 2026
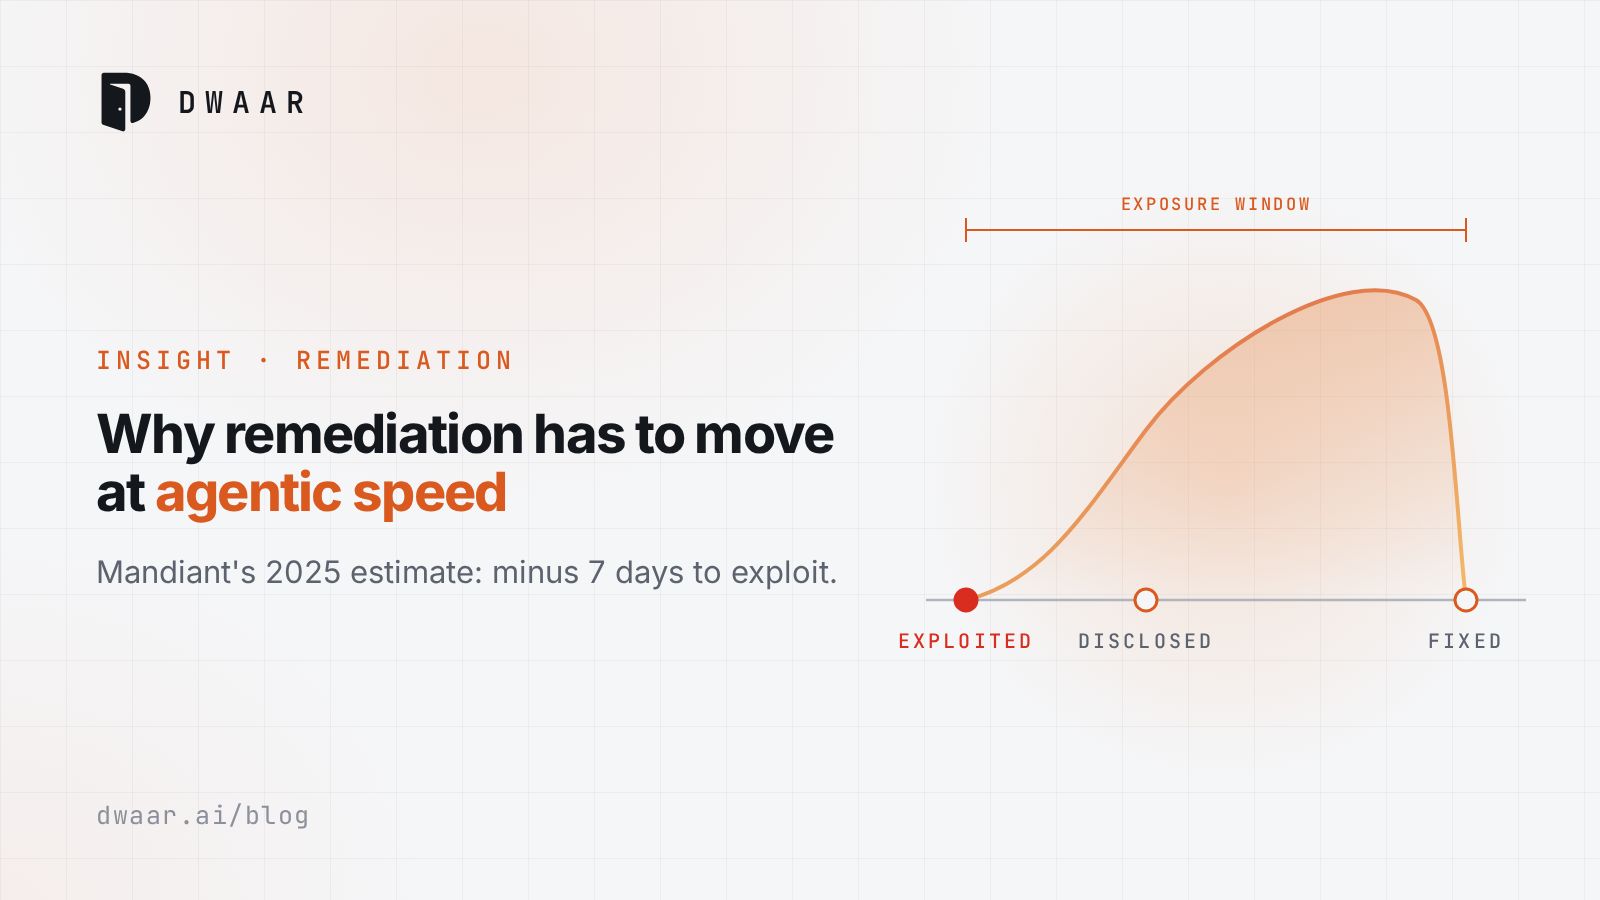
Why Remediation Has to Move at Agentic Speed
Mandiant estimates mean time to exploit at minus 7 days, while edge-device fixes reportedly take a median 32 days. Which patching steps agents can take over, and which stay with a human.
Ankush K · 8 min read
CVE-2026-33017: Langflow's Public Flow Endpoint Runs Unauthenticated Code, and No Stable Release Fixes It
An unauthenticated Langflow RCE has a public advisory and proof of concept, and as of March 19 no stable langflow release on PyPI carries the fix.
Ankush K · 7 min read