13 posts tagged with "Supply chain"
Attacks on the packages, images and tools you trust.
View All TagsDwaar Blog
August 2026
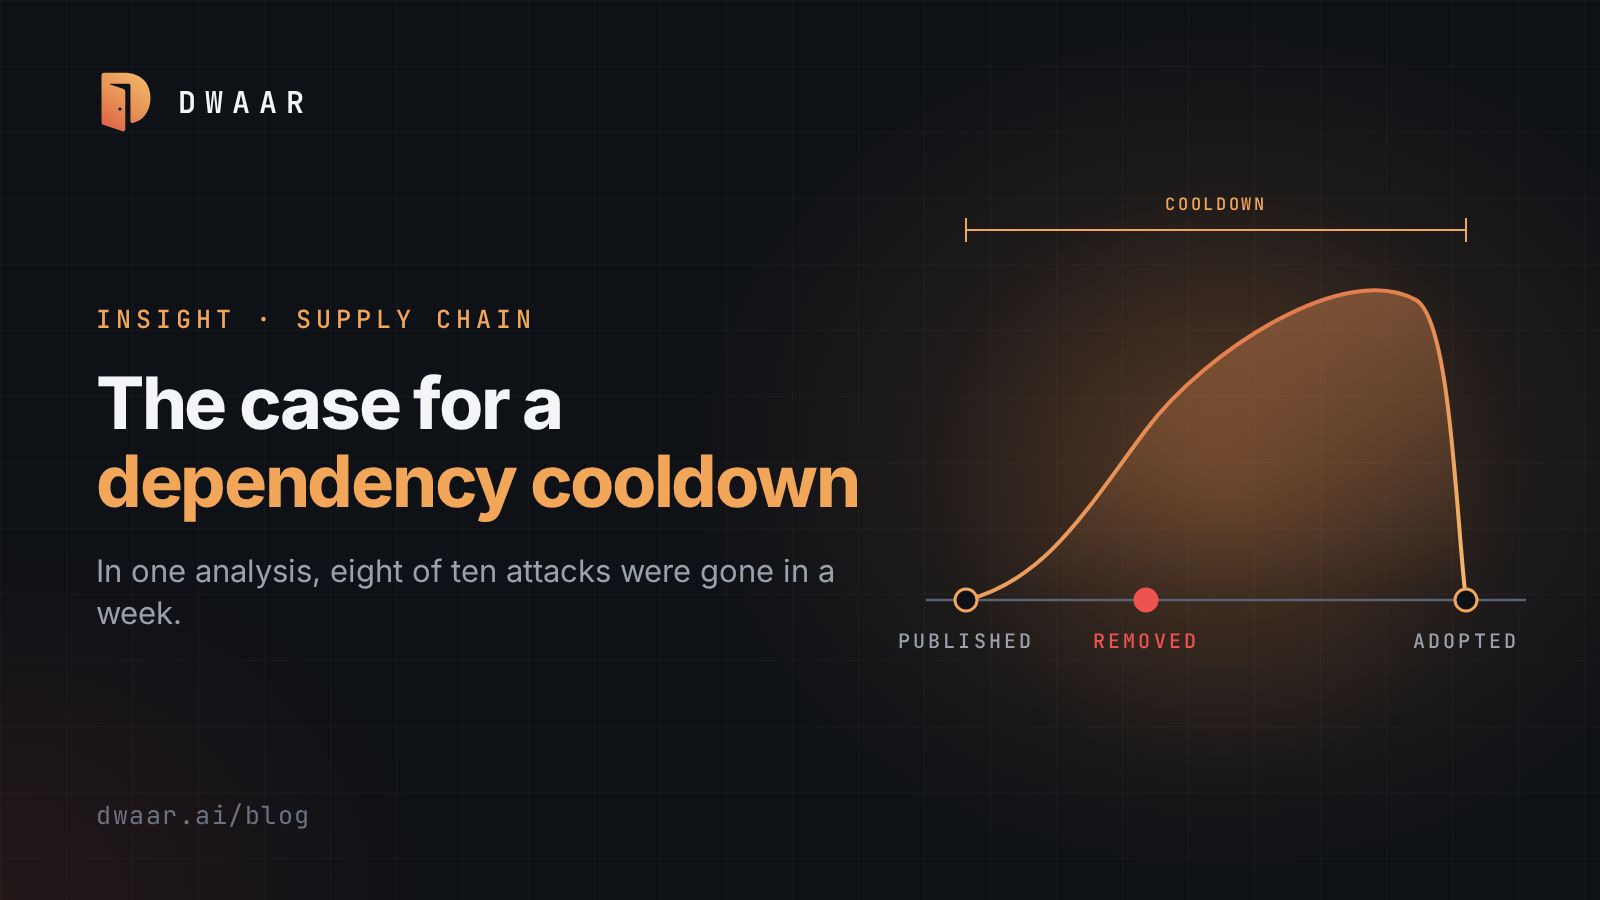
The Case for a Dependency Cooldown
In one analysis of ten supply chain attacks, eight were removed in under a week. Why waiting before adopting a new version works, where it fails, and how to exempt security fixes.
 Ankush K · 9 min read
The keyv and cacheable npm Worm: Valid Provenance, Poisoned Source
A malicious keyv 6.0.0 reached npm through the project's real release workflow with valid provenance, then a worm spread through the Cacheable packages and hundreds more.
Ankush K · 9 min readJuly 2026
The Hugging Face Breach Is a Preview: Why Guardrails Must Live Outside the Model
Hugging Face's July 2026 incident shows what happens when the model supply chain itself is compromised. Scope-based identity isn't enough — agentic security needs zero-trust, intent-based identity and a physically separate guardrail engine.
Ankush K · 12 min read
AsyncAPI: Trojaned npm Packages With Valid Provenance
Five malicious @asyncapi npm versions shipped on 2026-07-14 through the project's own release pipeline, with valid provenance and no install script.
Ankush K · 10 min readJune 2026
Cordyceps: Exploitable GitHub Actions Workflows in Over 300 Repositories
Researchers report more than 300 exploitable repositories from a class of GitHub Actions flaws, including chains of individually valid workflows. No CVE, no versions to patch, no in-the-wild use reported.
Ankush K · 8 min read
Your CI Pipeline Is Production
CI jobs hold publish tokens, cloud credentials and repository write access. Moved tags, pull_request_target, shared caches and stored secrets have all turned that authority on users.
Ankush K · 9 min read
A vLLM Dockerfile Dependency Confusion: How One --extra-index-url Put the Official Image at Risk (GHSA-jrf6-vqxq-pjv2)
vLLM's Dockerfile mixed --extra-index-url with uv's unsafe-best-match, exposing vllm/vllm-openai builds below 0.22.1 to dependency confusion. The advisory reports no exploitation.
Ankush K · 8 min read
Miasma: How a Compromised Red Hat GitHub Account Published Malware Through npm Trusted Publishing
Red Hat says a compromised GitHub account pushed unauthorized commits. Reports say an added workflow then published malicious @redhat-cloud-services packages through npm trusted publishing.
Ankush K · 8 min readMay 2026
Nx Console 18.95.0: A Trojaned VS Code Extension Published With Stolen Credentials
Nx Console 18.95.0 was trojaned on 18 May 2026 using a developer's leaked GitHub credentials. What it stole, how to check your machines, and what GitHub has and has not said.
Ankush K · 9 min read
The TanStack npm Compromise: Actions Cache Poisoning and a Stolen OIDC Token Behind a Legitimate Trusted Publisher
On 2026-05-11, 84 malicious versions of 42 @tanstack npm packages shipped through TanStack's real trusted publisher, using a poisoned Actions cache and an OIDC token read from runner memory.
Ankush K · 9 min readApril 2026
A Vulnerable Package and a Malicious Package Are Different Problems
The OSV and GitHub records for the poisoned axios and LiteLLM releases list no CVE. Malicious packages need a different signal, clock and response from vulnerable ones.
Ankush K · 9 min read
The axios npm Hijack: When the Attack Goes Through the Maintainer
Two axios releases on npm carried a RAT through a postinstall hook in a new dependency, with no CVE and no change to axios source. What to check, and what lockfiles and release age buy you.
Ankush K · 8 min read