8 posts tagged with "Vulnerability management"
Deciding what to fix first, and why severity alone cannot.
View All TagsDwaar Blog
November 2026
October 2026
Stop Counting Vulnerabilities
A count of open findings measures backlog, not risk. Measure time to fix what is exploited or exposed, coverage of what you own and repeat findings, and know how each gets gamed.
 Ankush K · 9 min read
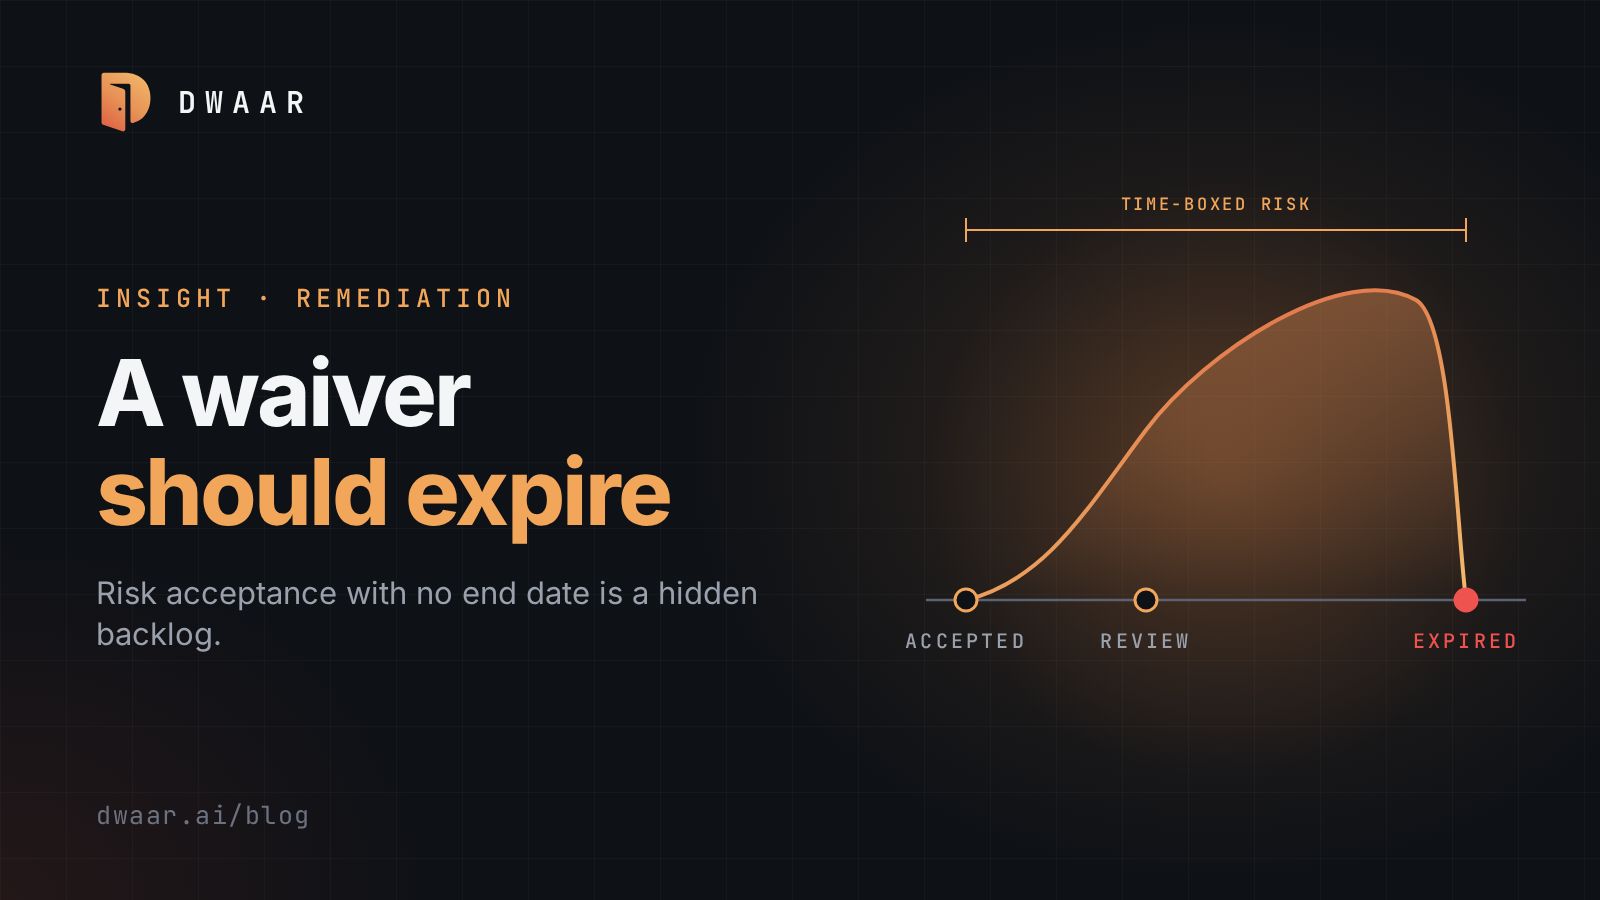
A Waiver Should Expire
Risk acceptance with no end date is a hidden backlog. What a waiver should record, what should reopen it, and why suppressing noise is a different decision.
Ankush K · 8 min readSeptember 2026
May 2026
April 2026
March 2026
CVSS Is Not Risk: How to Use EPSS and KEV
CVSS Base measures severity, KEV records confirmed exploitation and EPSS forecasts it. How to combine the three into a queue, and where all of them stop.
Ankush K · 8 min read
Why Scanning Alone Is Not a Security Program
A scan report is a list, not a decision. Using NIST guidance, Verizon's 2025 DBIR and the Equifax record, this post lays out what has to sit between the two.
Ankush K · 8 min read